Identity + Authentication + Authorization + Enforcement + Policy

Secure By Design.
Made Simple.

Aranya is an edge-native embedded software toolkit for building resilient, secure controls directly into applications and systems, enabling teams to define custom security policies with the Aranya DSL and enforce them alongside the resources they protect without centralized infrastructure or dependencies.

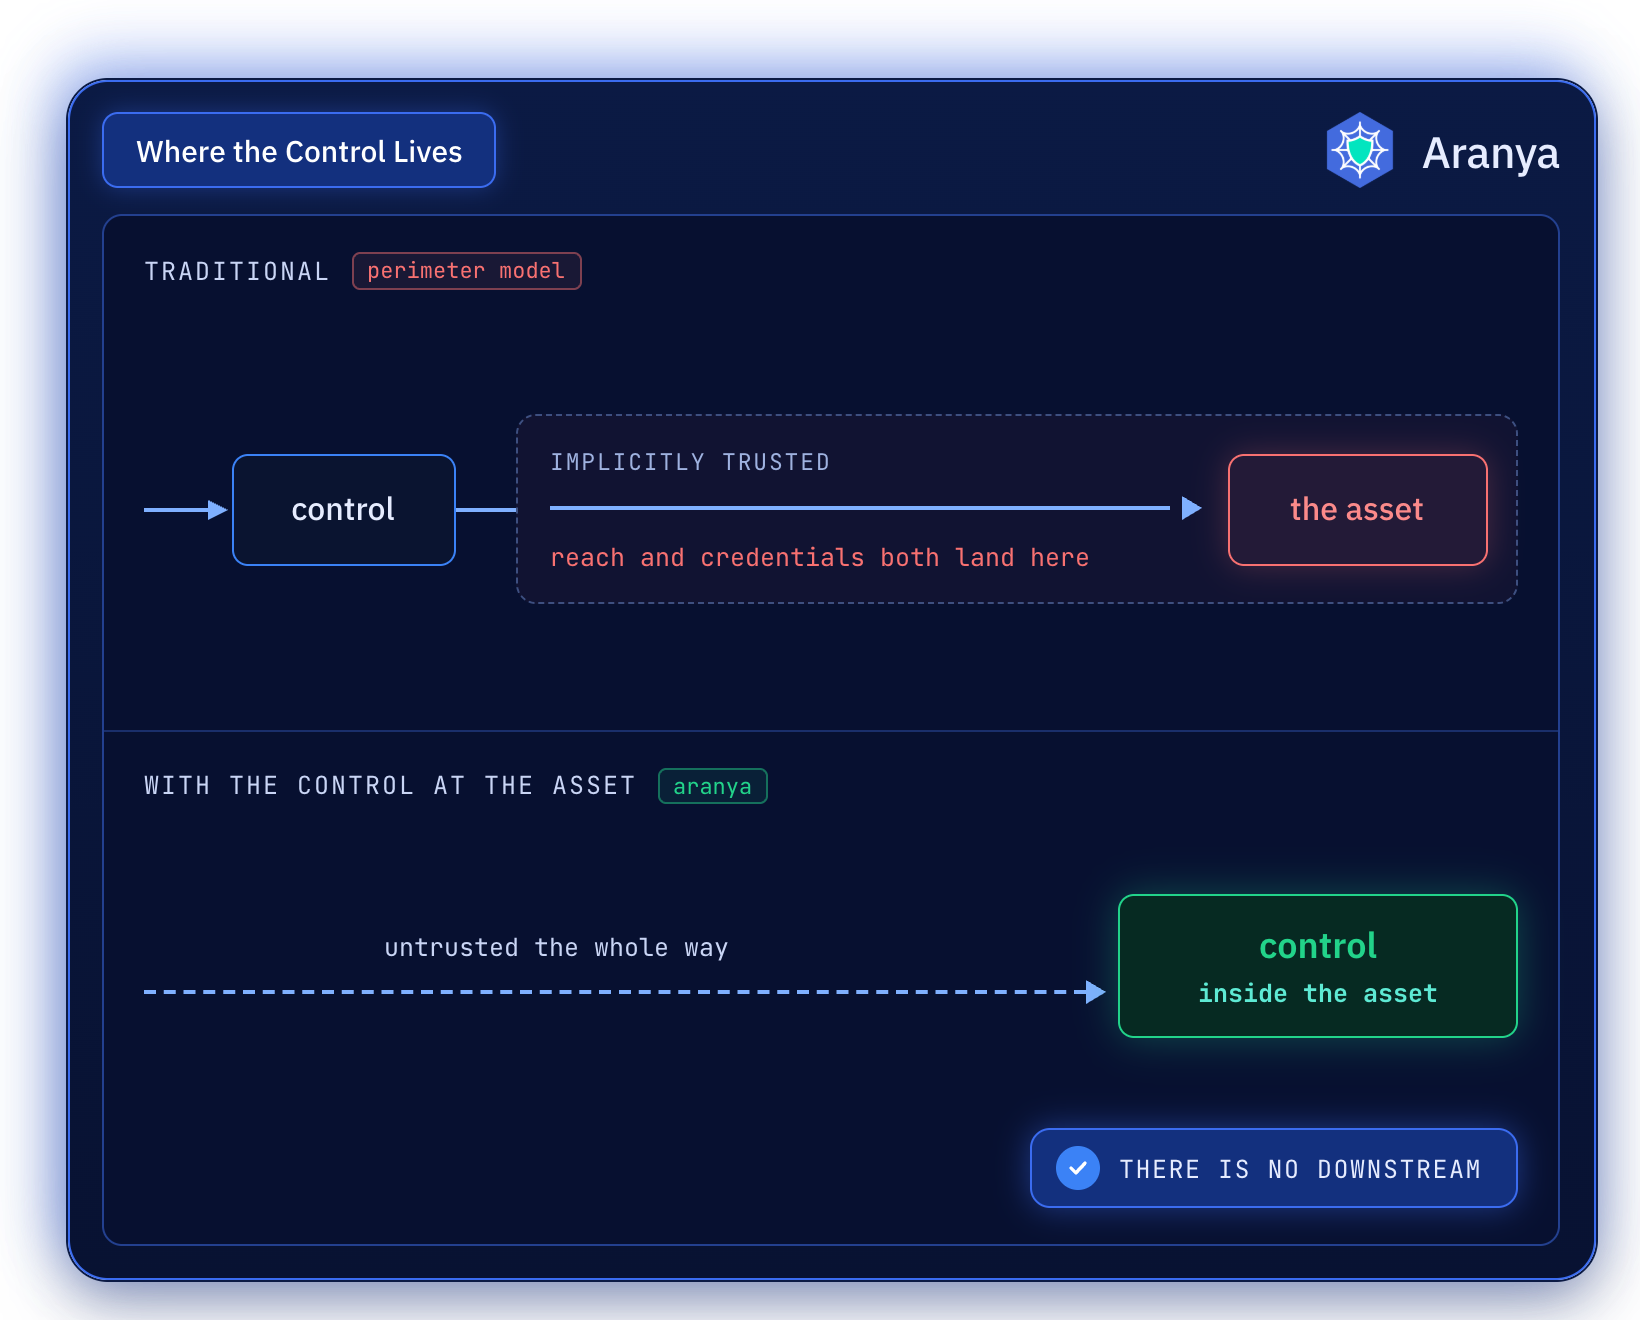
Diagram of Aranya identity, authorization, and policy enforcement embedded alongside system resources
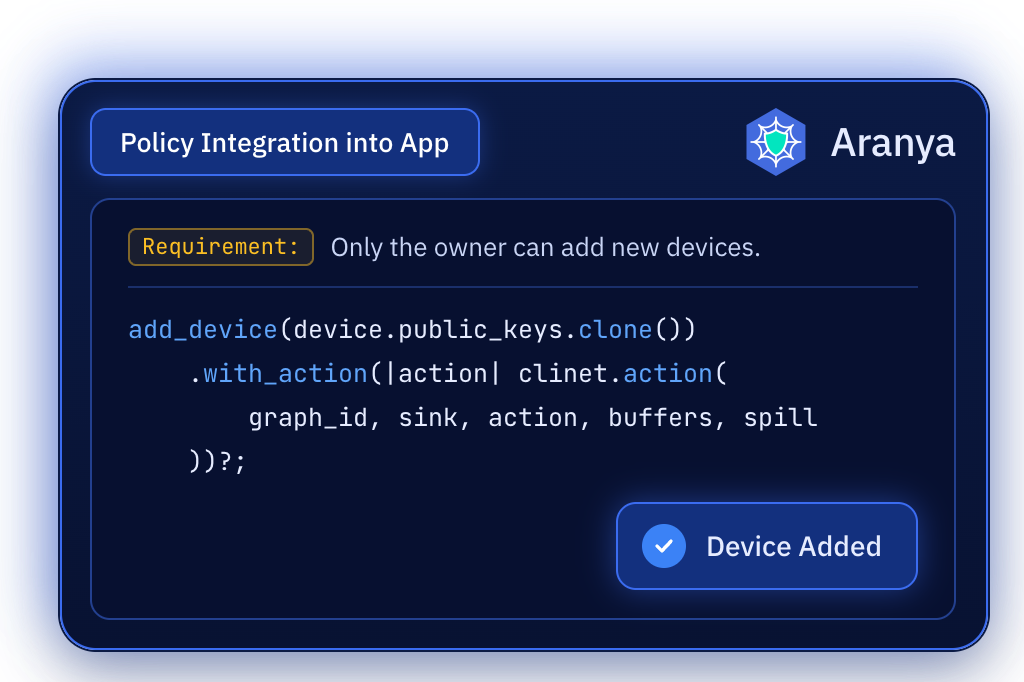
Aranya policy integration interface
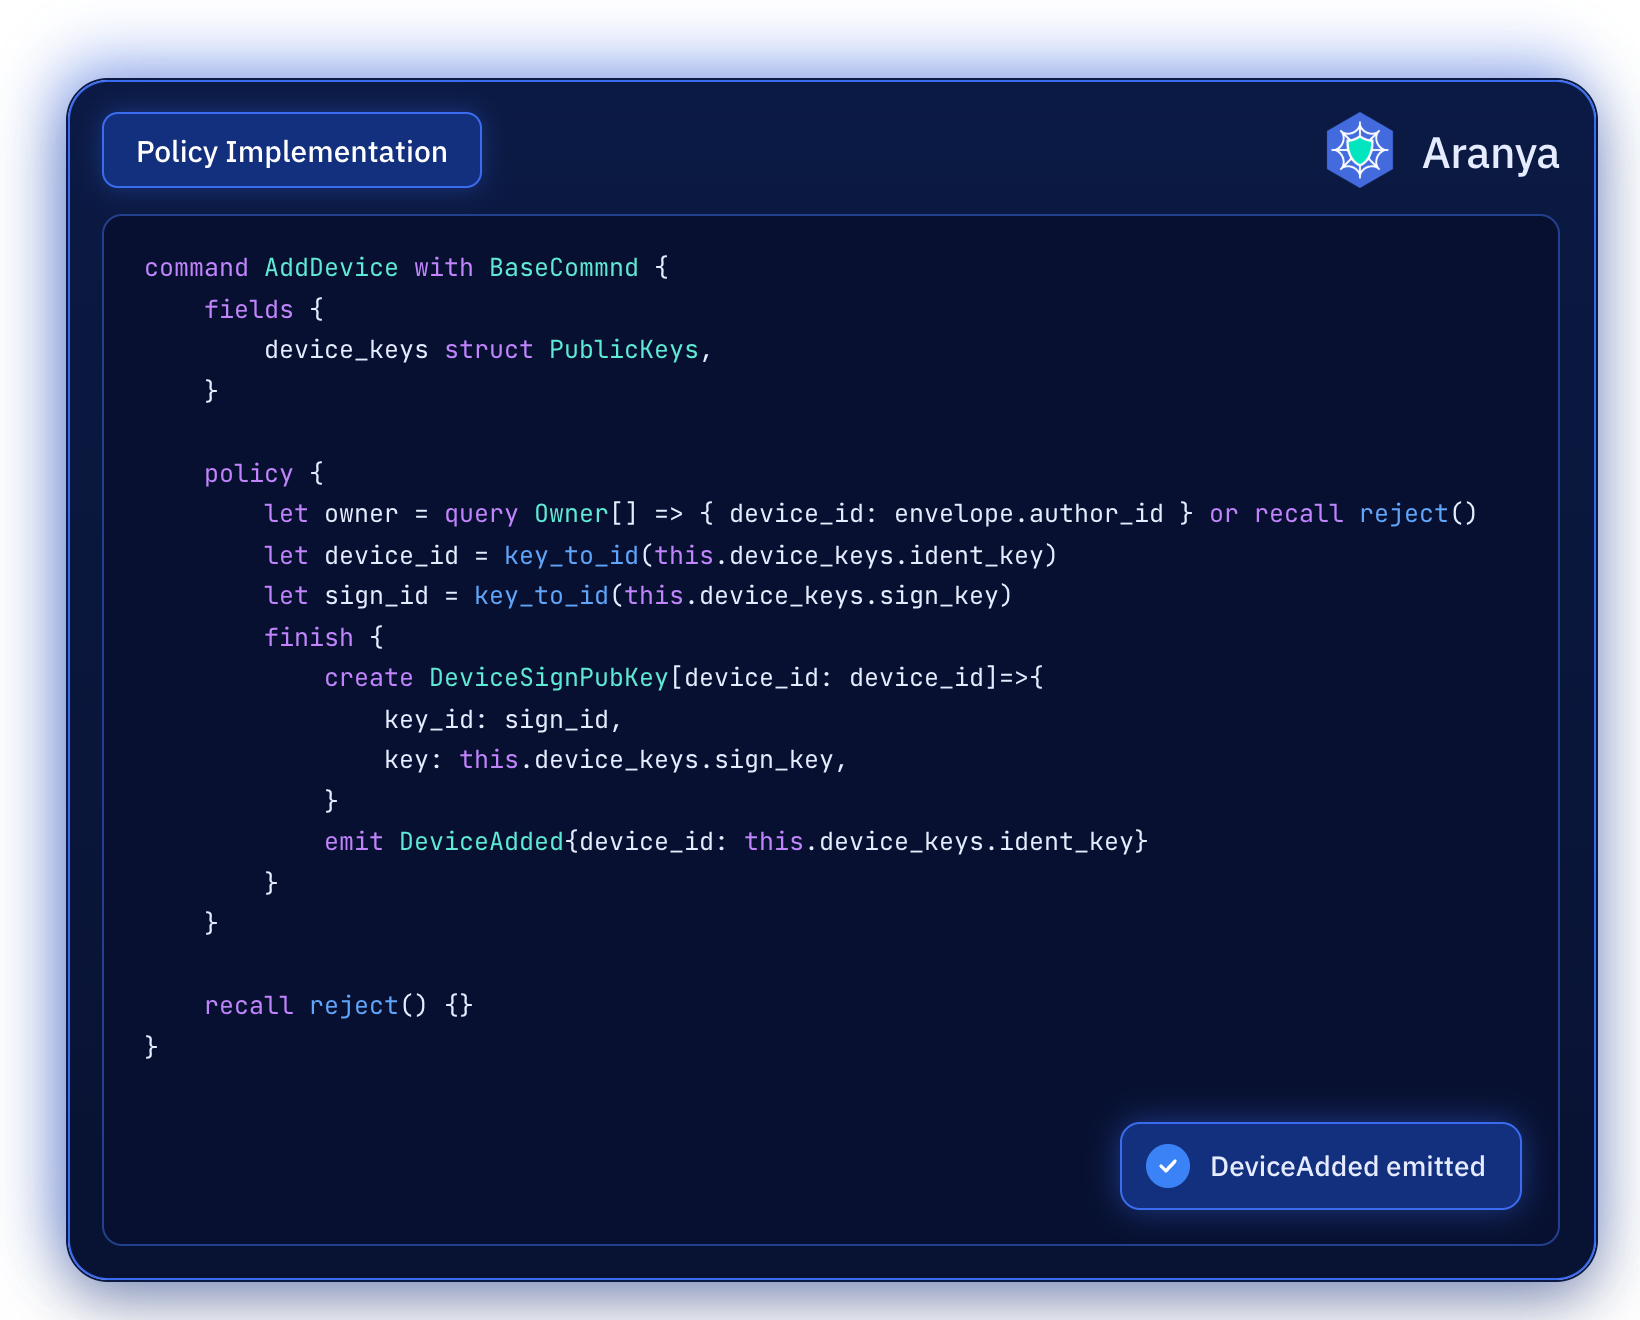
Aranya DSL policy implementation example
Customers
Defense Innovation Unit (DIU) logoSpace Development Agency (SDA) logoTrustPoint logoNorthrop Grumman logoSolitude Labs logoSyncStage logoU.S. Space Force logoRaytheon logoCollins Aerospace logoAir Force Research Laboratory (AFRL) logoRaft logoOmni Federal logoAccenture logoPlanet logoNational Reconnaissance Office (NRO) logoAxiom Space logo
Aranya security controls placed adjacent to the resources they protect
Embedded Security

Security Controls Where They Matter Most

Aranya puts security controls adjacent to the resources they protect, enabling developers to embed identity, access, encryption, and policy enforcement directly into their commercial solutions.

Instead of relying on third party security products and network security, Aranya provides the building blocks to make security part of the architecture from the start.

Developer Toolkit

Built for Developers. Engineered for the Edge.

Aranya provides an embedded toolkit for creating secure, centralized or decentralized applications that continue operating across constrained, disconnected, and contested environments.
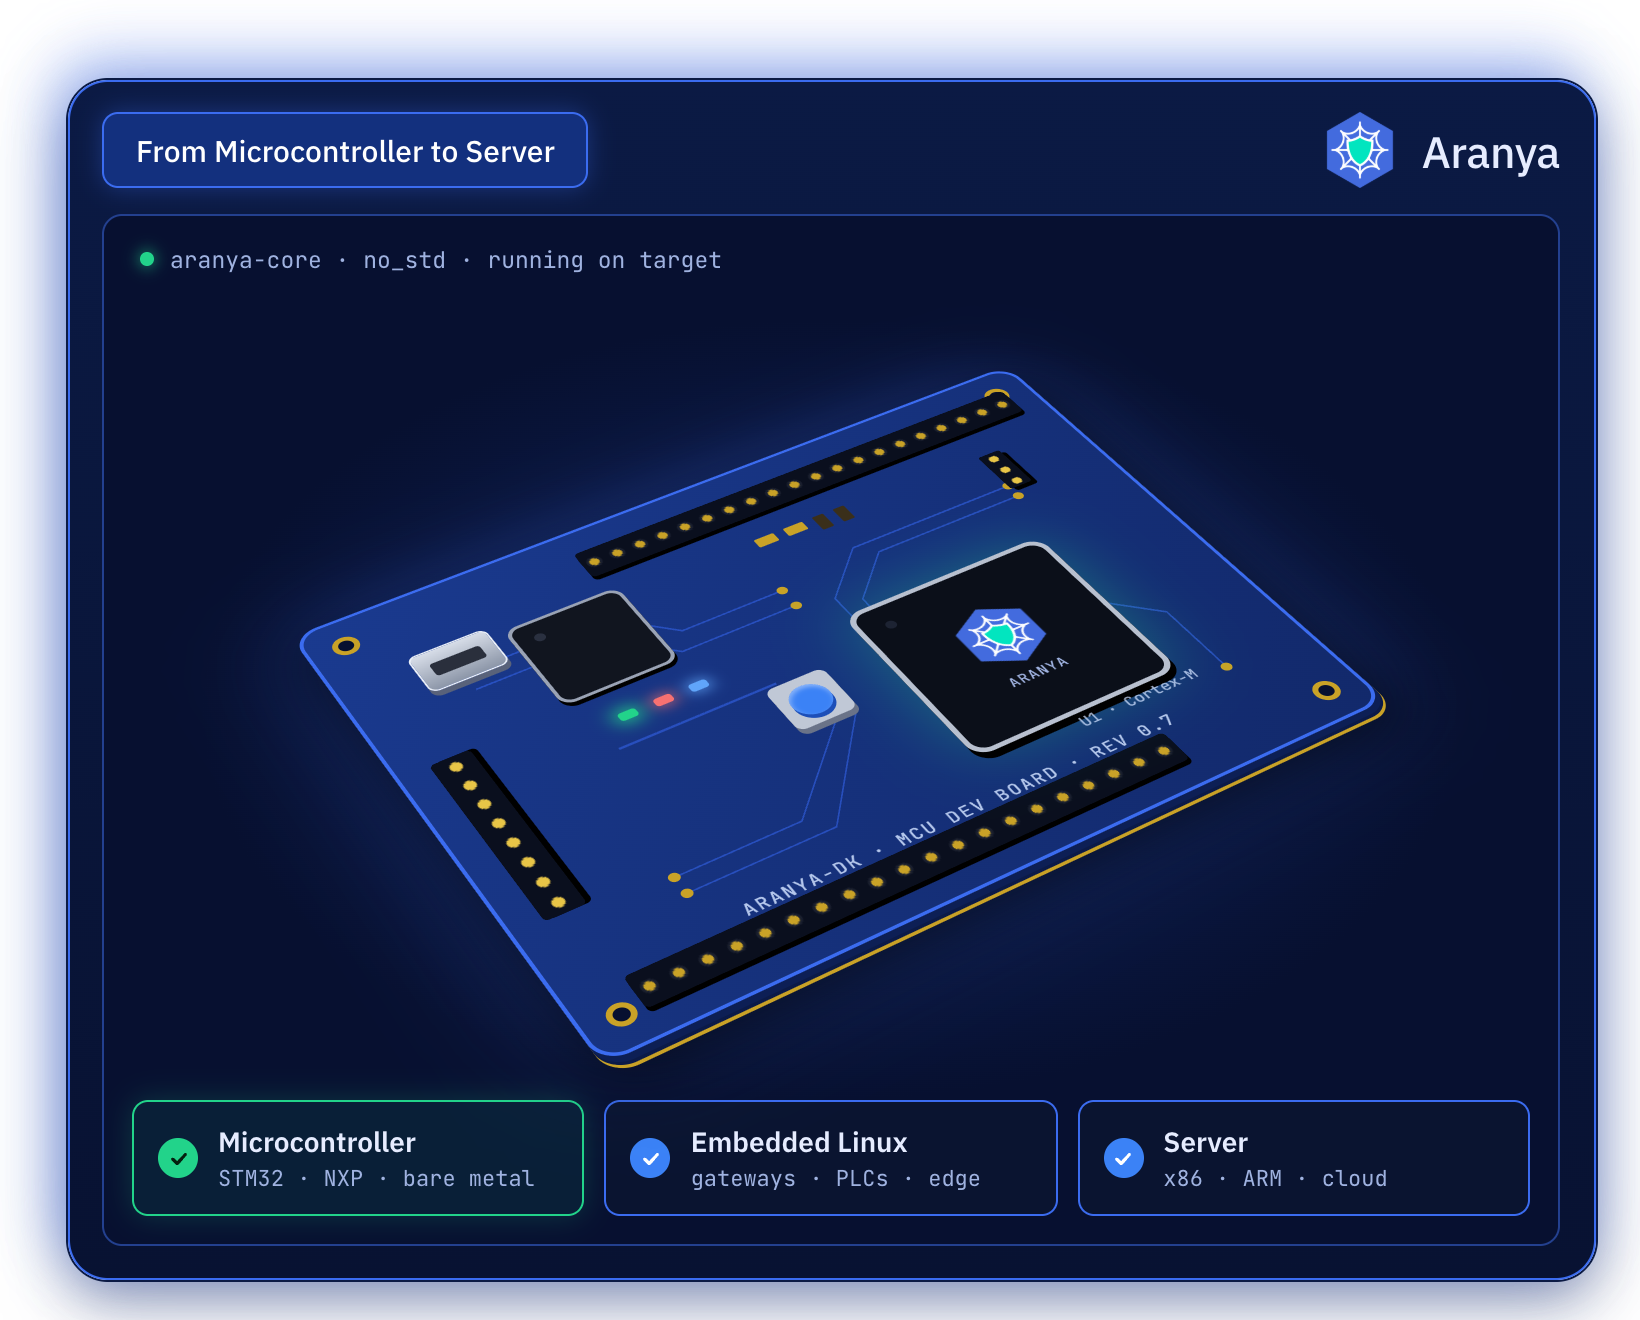
Aranya embedded toolkit running on a developer board
Icon

Aranya DSL

Define custom security policies as code and decouple policy from implementation, making controls easier to build, maintain, audit, and update.
Edge-Native Controls

Co-locate controls with system resources so identity, authorization, and policy decisions can be enforced where operations actually occur.
Decentralized by Design

Eliminate dependence on centralized servers for critical security decisions and maintain trusted operations when connectivity is degraded, intermittent, or unavailable.

Core Capabilities

Everything You Need to Build Resilient Controls

Aranya provides the core capabilities developers need to build secure, resilient applications that maintain trusted operations across distributed, constrained, and disconnected environments.
Strong cryptographic identity

Unique identity creation for user, device, or resource resilient with attached policy based controls and lifecycle governance including revocation.
Asynchronous end-to-end encryption

Protect data across distributed applications without requiring continuous connectivity.
Automatic many-to-many state synchronization

Keep distributed state synchronized across authorized nodes and resources.
Low overhead & lightweight

Less than 500KB of RAM and less than 2MB of storage.
Serverless architecture

Remove centralized infrastructure, dependencies, and single points of failure.
Network disruption tolerant

Continue authorized operations when networks are offline, partitioned, or degraded.
Written in Rust

Built on a memory-safe systems programming language designed for performance and reliability.
Low latency

Line-rate encryption with enforcement decisions requiring fewer than 100 instructions.
Network and OS independent

Embed controls across heterogeneous systems without tying your architecture to a specific operating system or network.

One Toolkit.
Multiple Mission-Critical Use Cases.

Aranya gives developers a unified toolkit for securing applications with data-level microsegmentation, cryptographic identity and access controls, and automatic state synchronization.

‍
Designed for disrupted and disconnected environments, Aranya allows authorized nodes to continue operating independently and securely synchronize when connectivity returns.

Key Benefits

Build Faster. Operate for Less. Adapt with Confidence.
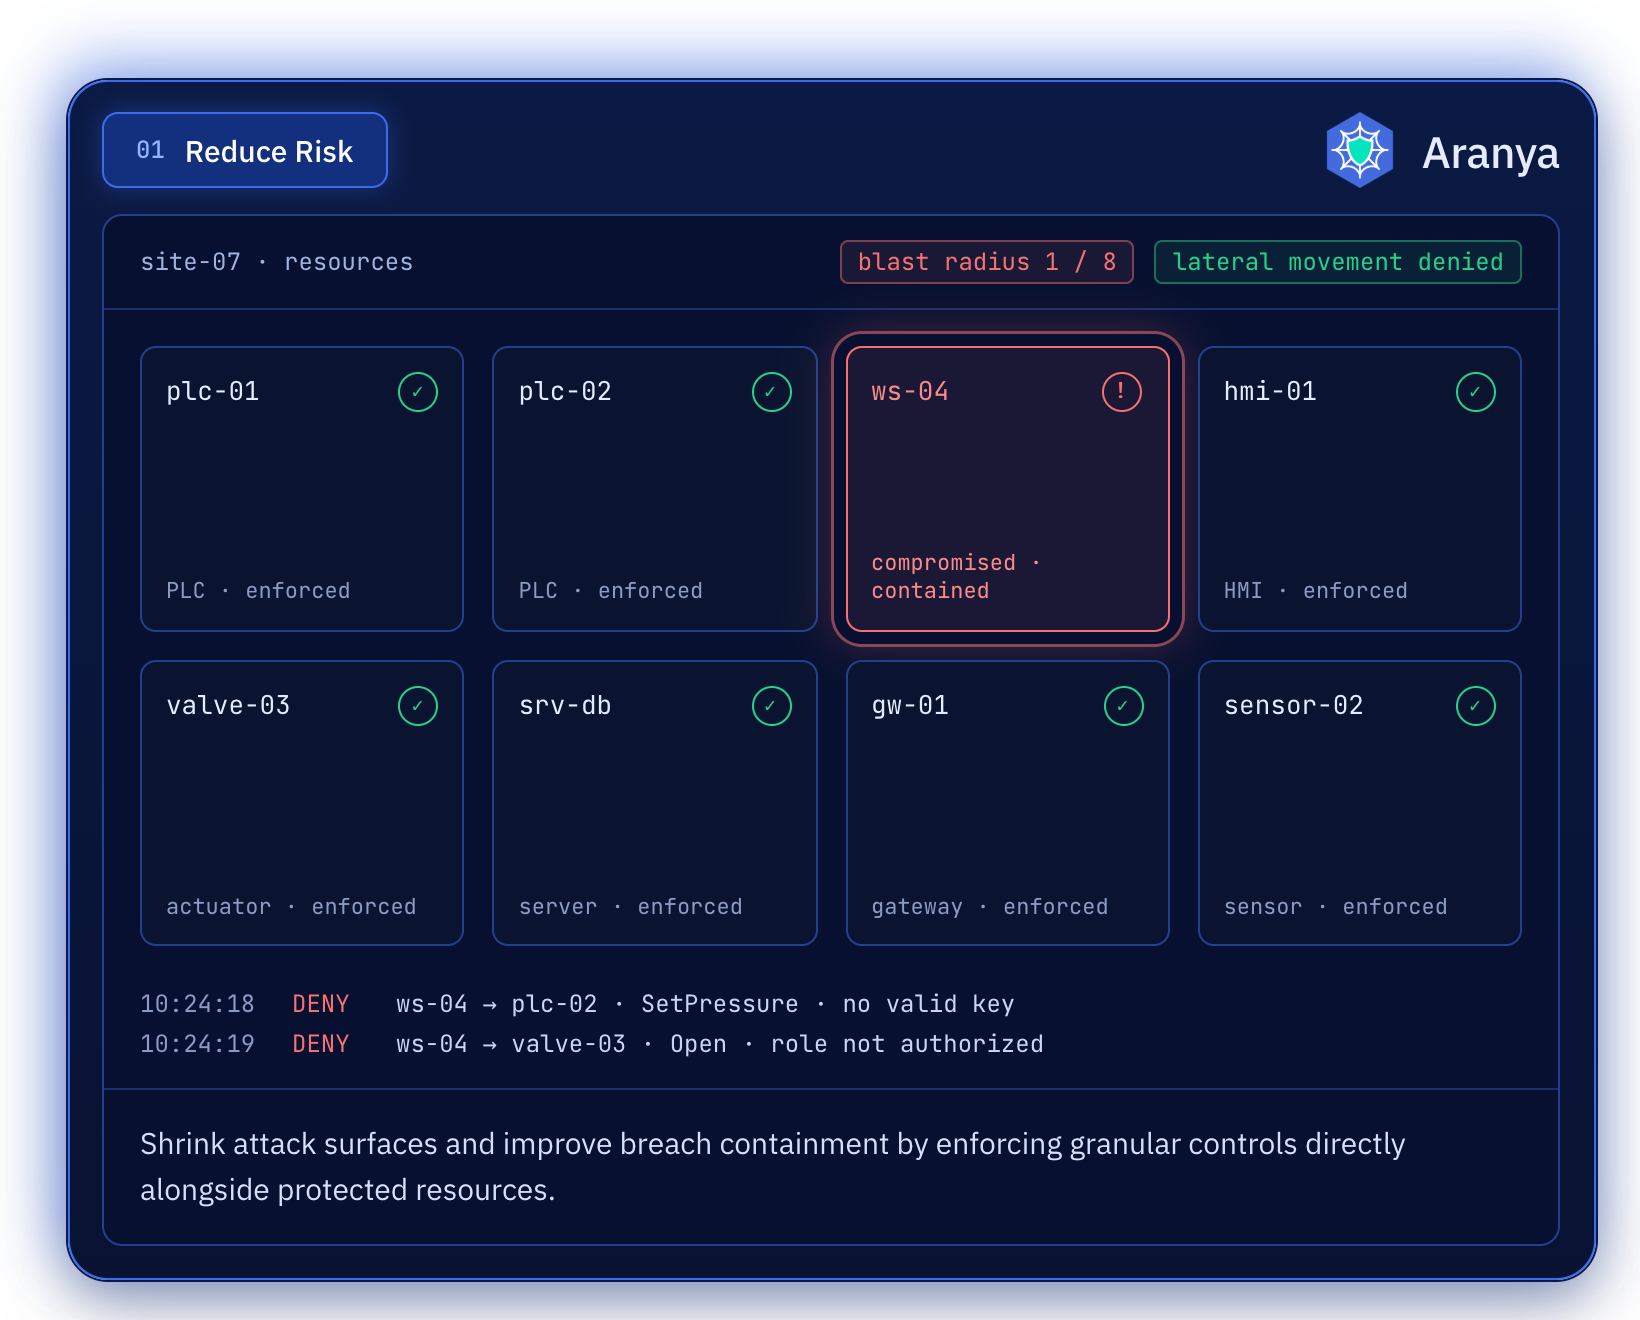
Illustration of reducing risk with granular controls and breach containment

Reduce Risk

Shrink attack surfaces and improve breach containment by enforcing granular controls directly alongside protected resources.
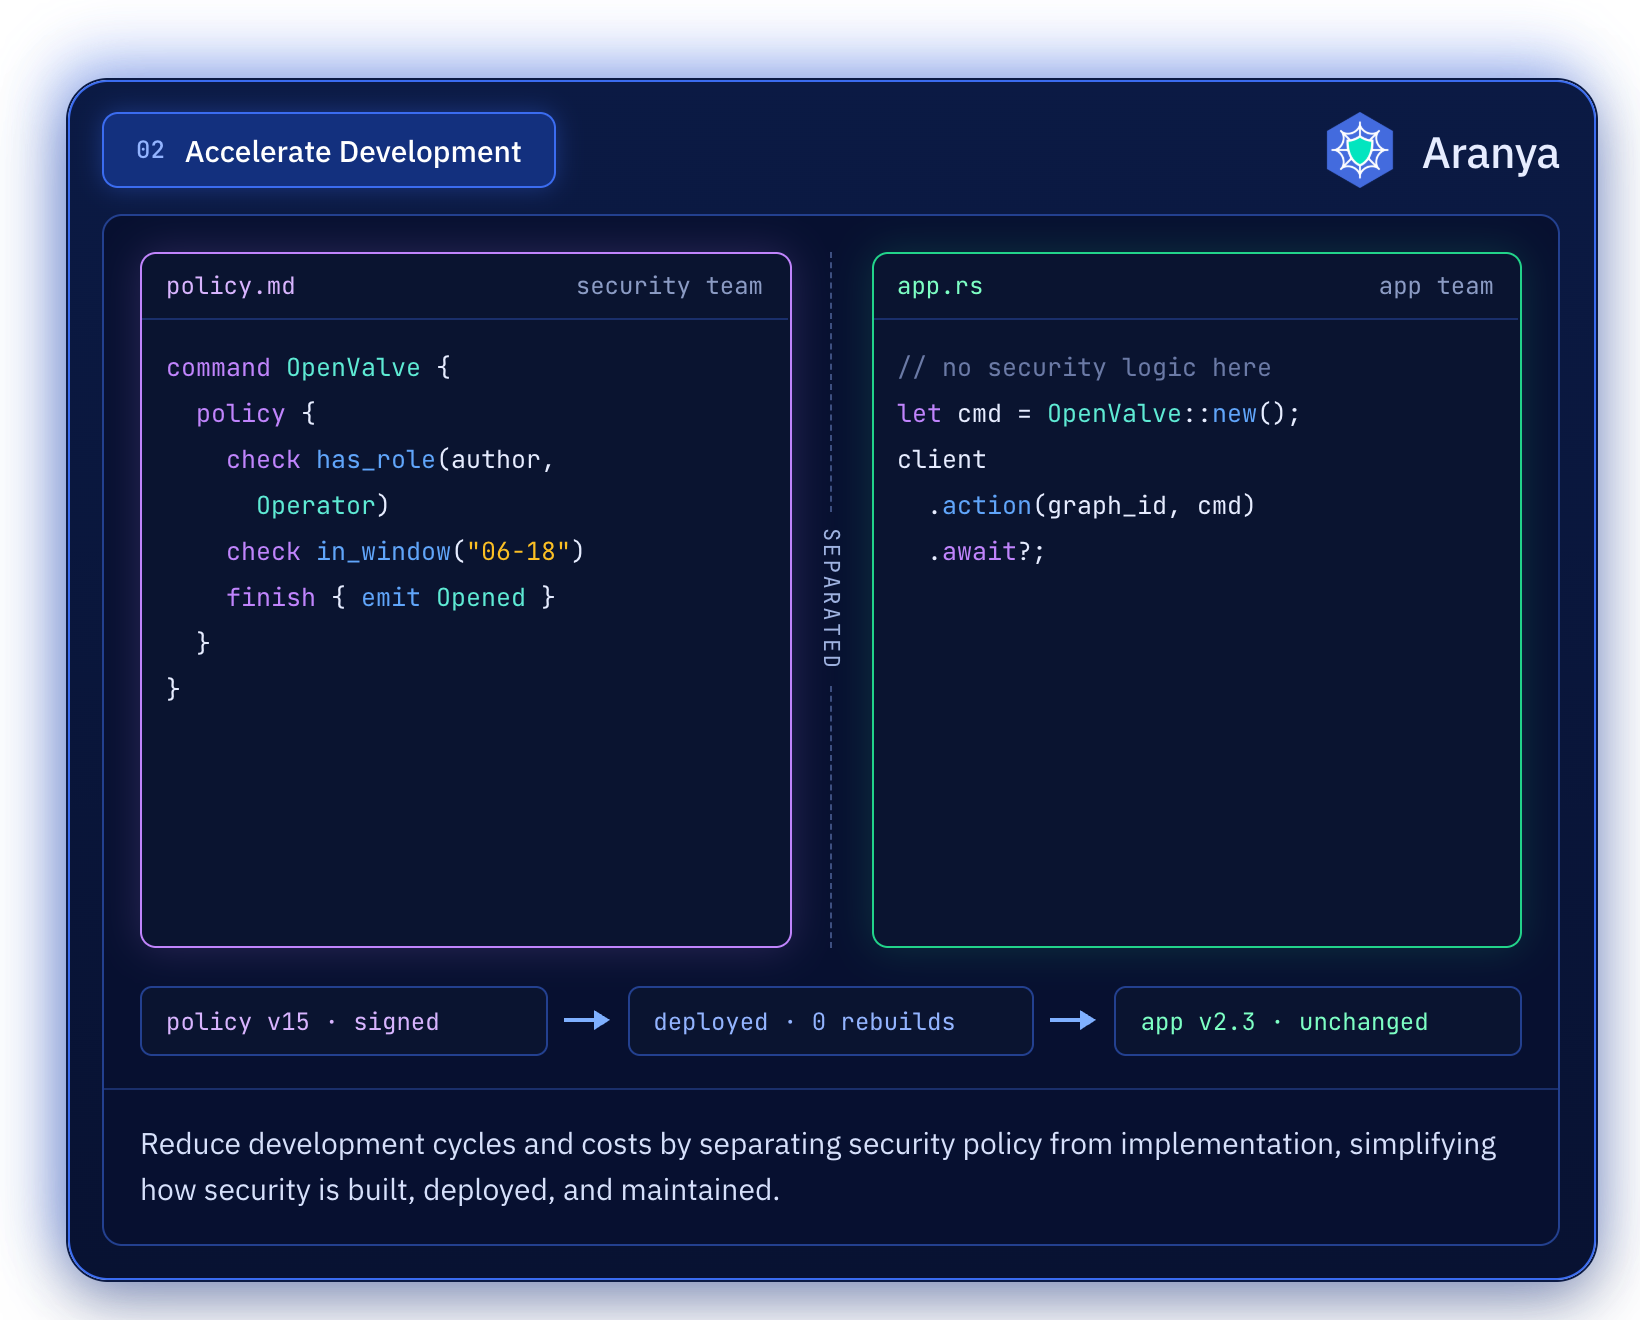
Illustration of accelerating development by separating policy from implementation

Accelerate Development

Reduce development cycles and costs by separating security policy from implementation, simplifying how security is built, deployed, and maintained.
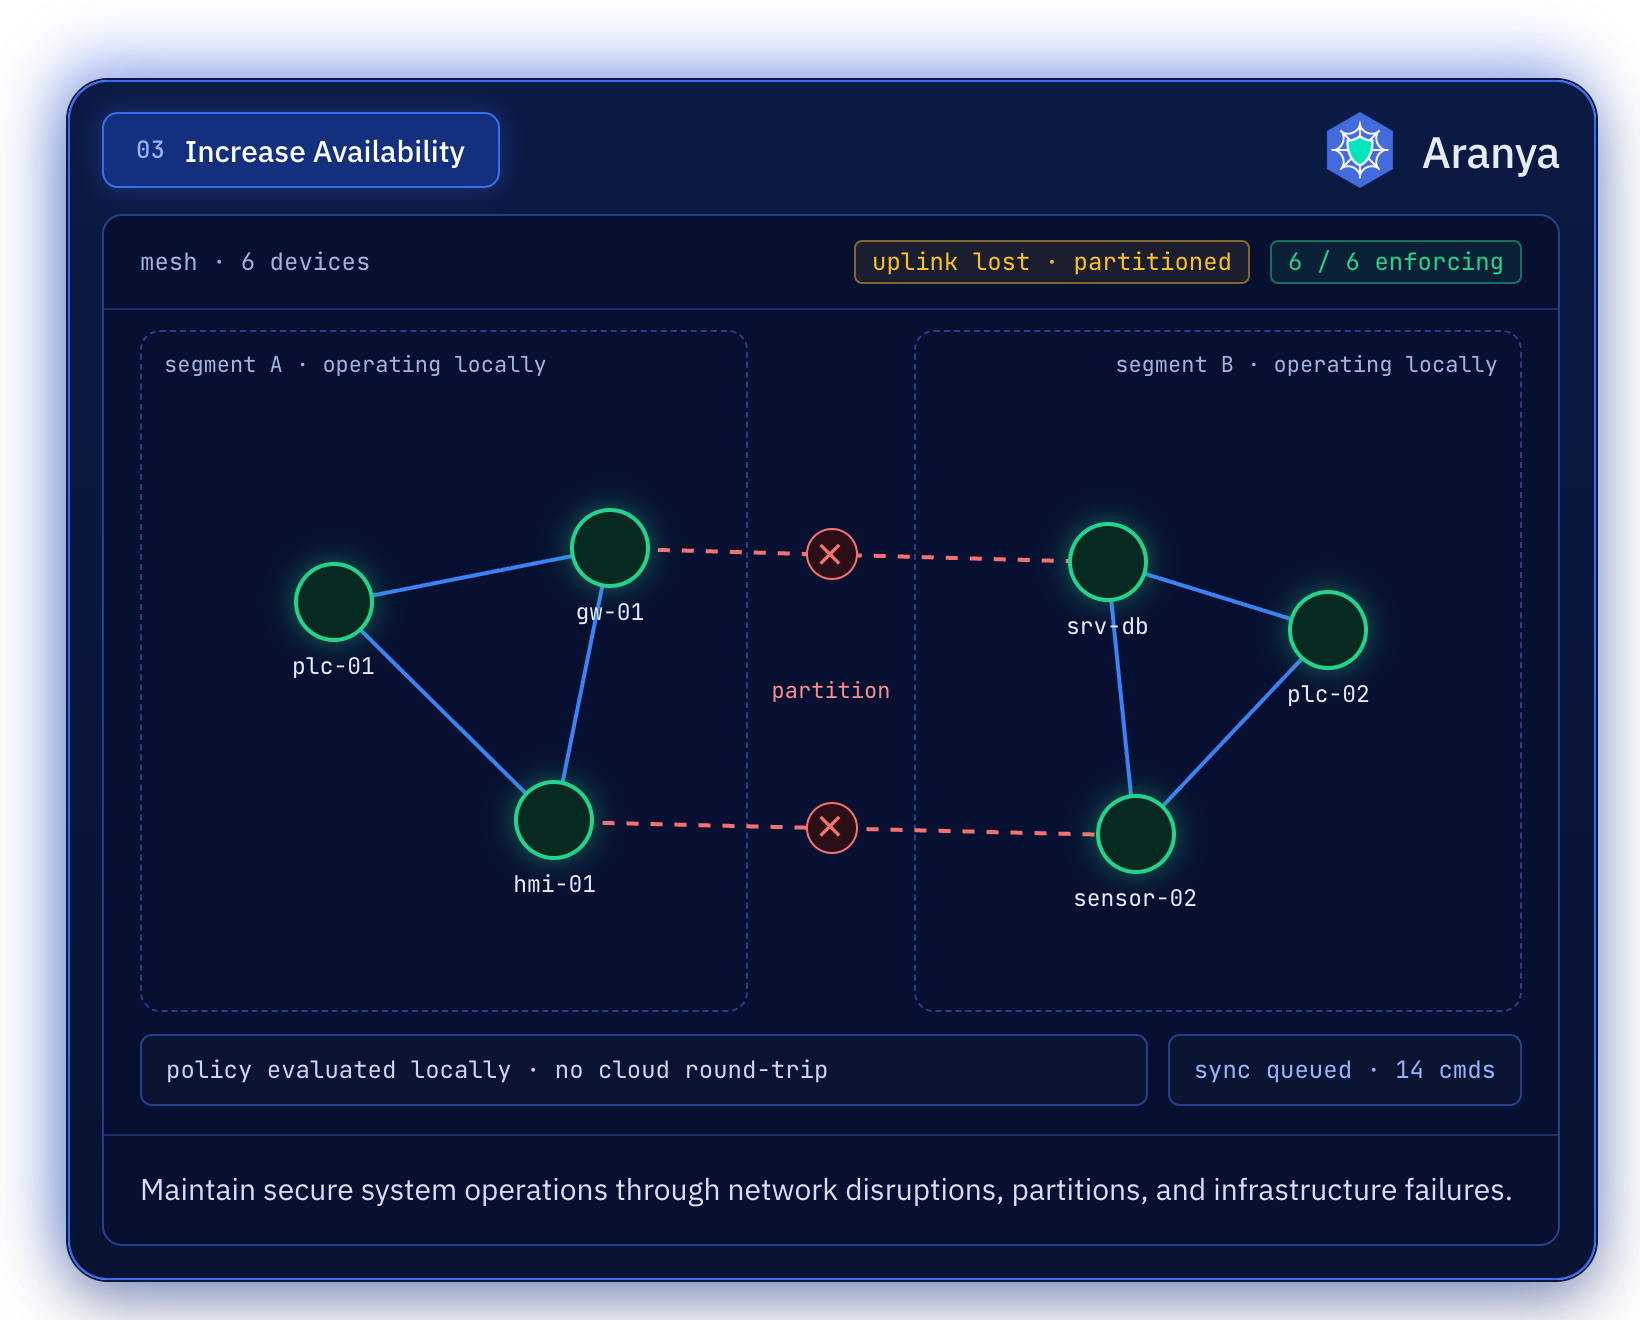
Illustration of increased availability during network disruptions

Increase Availability

Maintain secure system operations through network disruptions, partitions, and infrastructure failures.
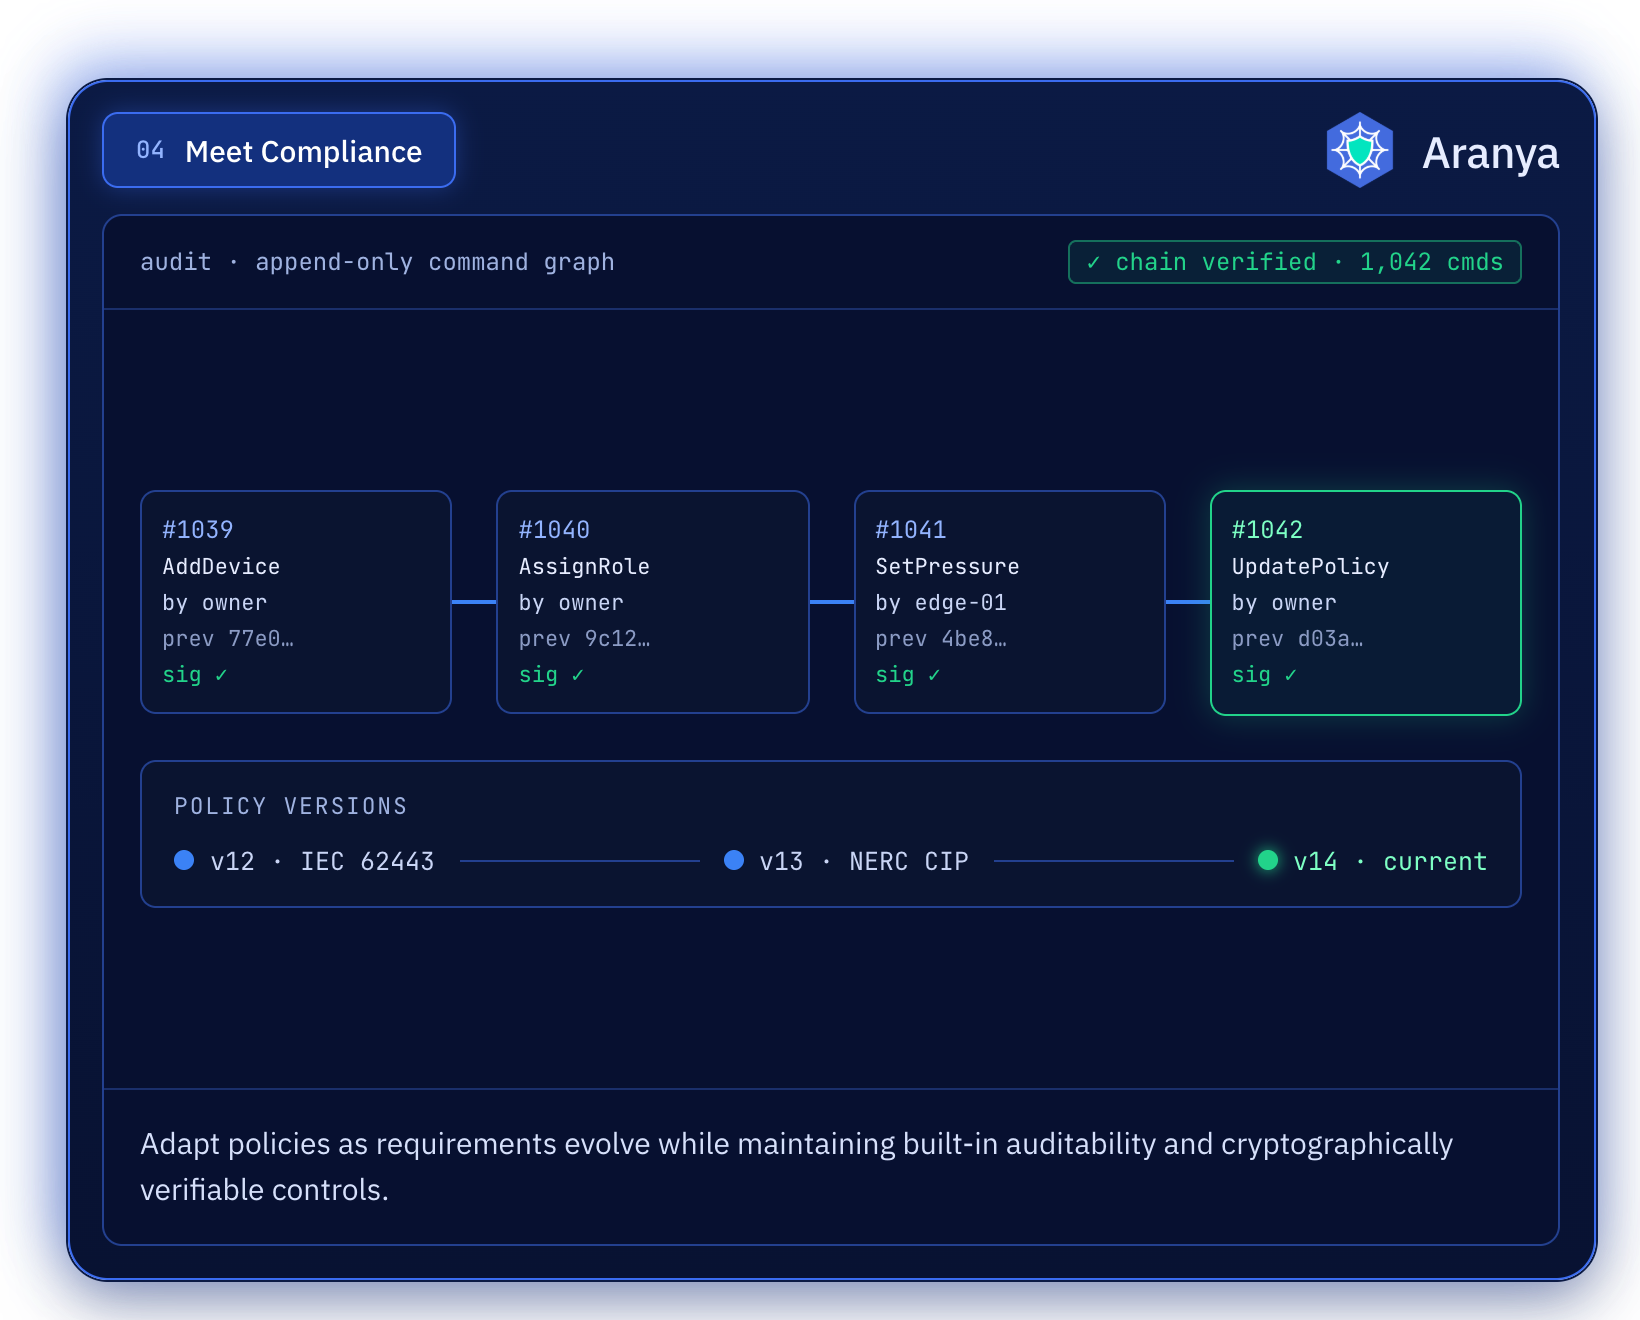
Illustration of meeting compliance with auditable, cryptographically verifiable controls

Meet Compliance

Adapt policies as requirements evolve while maintaining built-in auditability and cryptographically verifiable controls.

case studies

Aranya in Action

See how Aranya is being deployed and validated across space, defense, and critical infrastructure environments to deliver decentralized security, resilient operations, and cryptographically enforced access controls.

Solitude Labs: Zero Trust Edge Enforcement for Critical Infrastructure

Solitude Labs is integrating Aranya to create a resilient, policy-enforced security mesh for distributed utility infrastructure. Aranya enables identity and access controls at both the application and network security layers, with cryptographic enforcement supporting fine-grained RBAC/ABAC and dynamic microsegmentation across OT/IT environments. The decentralized architecture supports low-latency peer-to-peer operations during intermittent connectivity while reducing centralized key dependencies and single points of failure.

Raytheon BBN: Decentralized Security for Contested Space

Raytheon BBN partnered with SpiderOak Mission Systems to integrate Aranya with D4 Secure for resilient communications across proliferated low-Earth orbit satellite networks. Aranya provides decentralized access controls, automated key lifecycle management, and an immutable record of events designed to persist as constellation topologies change. Combined with D4's autonomous cross-link routing, the architecture supports trusted mesh communications and resilient data propagation in disrupted and contested environments.

SDA M3 Microsegementation: Multi-Party Data Segmentation for Space Systems

Under the Rapid Resilient Command & Control initiative, SpiderOak demonstrated zero-trust cybersecurity mechanisms for resilient space command, control, and communications. Aranya enabled cryptographically enforced data access and topic-level security, allowing microsegmentation across distributed space and ground communications. By enforcing identity and policy at message origination, the implementation strengthened BMC3 application communications against lateral movement and interception.

DIU Hybrid Space Architecture: Variable Trust Policy for On-Orbit Space Controls

SpiderOak deployed an Aranya-based application in a live on-orbit demonstration designed to protect the DoD's Hybrid Space Architecture against unauthorized commands and data interception. Working with Terran Orbital, onboard policy controls cryptographically verified identity and authorization before executing a ground-issued image-capture command. The demonstration validated end-to-end cryptographic enforcement at the data layer under real operational and network constraints.

AFRL: USSF IdAM and Service Order Validation for Commercial Systems

Under an AFRL TACFI award, SpiderOak leveraged Aranya to provide a zero-trust control plane supporting the U.S. Space Force's Commercial Augmentation Space Reserve. The architecture translates contractual service definitions into policy-as-code and supports ABAC, delegated authority, and cryptographic validation of service orders across untrusted commercial networks. This enables auditable access to commercial space services while preserving strict trust boundaries.

Proven Flight Heritage

Aranya has been validated across multiple on-orbit deployments, demonstrating secure data protection under real-world SWaP and connectivity constraints. Deployments and integrations with Axiom Space/ISS, Ball Aerospace, and TrustPoint have demonstrated decentralized key management, data-layer end-to-end encryption, and secure storage and transmission across distributed space systems.

GET STARTED

Zero-trust, your way.

Compare our open source and commercial editions to see how they align with your zero-trust needs.
Aranya
What’s included:

Aranya

Aranya Core, Aranya Embedded, and Aranya Microsegmentation
Community support (documentation, forums, bug fixes, etc)
Aranya Commercial
What’s included:

Aranya Commercial

Aranya Core, Aranya Embedded, and Aranya Microsegmentation
Community support (documentation, forums, bug fixes, etc)
Technical support (phone, email)
Verified builds